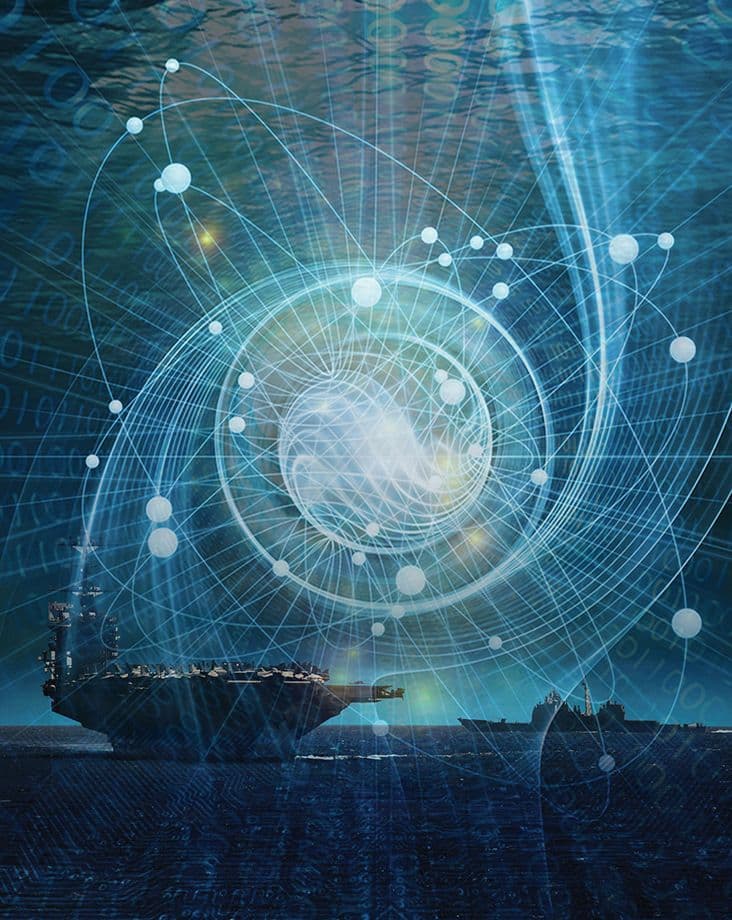
A graphic concept of quantum technology depicts two ships at sea in the background and a large, stylized molecule in the foreground. Naval Information Warfare Center (NIWC) Pacific’s scientists and engineers are leading quantum research, collaboration, and training among warfare centers. (U.S. Navy illustration by NIWC Pacific)
The Pentagon’s Quantum Race Needs a Warfighter’s Scorecard
Last updated 06:29 AM EDT • Read time: 6m
A $350 million computing initiative and a military-wide cryptographic transition serve different purposes. Both must be measured against the mission, not the milestone.
The Pentagon is putting money behind tomorrow’s quantum computers while racing to protect today’s military networks from what sufficiently advanced quantum computers could eventually do to them. Those efforts are technically different. This week, they arrived in the headlines almost together.
On October 8, the Department of War announced roughly $350 million in quantum computing initiatives. On October 1, the National Security Agency announced new post-quantum requirements for National Security Systems. The juxtaposition raises a more useful defense question than who has the most qubits or the greenest transition dashboard: What will actually work when a commander needs it?
A useful quantum computer for materials research is not necessarily a machine capable of breaking today’s public-key cryptography. Building one and defending against the eventual risks of the other involve different technology, budgets, and timelines. But both efforts can stumble over the same management habit: mistaking evidence of progress for evidence of mission value.
The first test: turn computation into something the services can use
The new package includes approximately $200 million in DARPA funding and a conditional loan commitment of up to $150 million for PsiQuantum’s manufacturing and prototyping work in California. The proposed loan is not money already disbursed. DARPA, meanwhile, has advanced Atom Computing, Diraq, IBM, and IonQ to the final stage of its Quantum Benchmarking Initiative, alongside Microsoft and PsiQuantum.
That advancement is meaningful, but it is a verification assignment, not a declaration that a useful fault-tolerant machine has been delivered. DARPA’s stated goal is to determine whether a quantum computer whose computational value exceeds its cost can be built by 2033. In Stage C, government evaluators will examine whether the proposed machines can actually be constructed and operated as intended.
The Pentagon’s announcement singles out chemistry, materials science, and physics as possible routes to military advantage. Consider a proposed heat-resistant component. A quantum calculation might predict a better material, or eliminate a poor candidate before engineers waste years testing it. That would be valuable. But the calculation earns acquisition credit only after experiments validate the prediction, suppliers demonstrate repeatable production, and the finished component meets performance and cost requirements.
As NIST’s materials-validation work makes clear, computational predictions must be checked against measured properties. The planned DARPA application workshops, due to begin before January, should therefore start with the acquisition decision rather than the algorithm. What precisely must improve? What is the strongest practical classical baseline? What will the full calculation cost once error correction and supporting hardware are counted? Who will test the resulting material or process, and who could manufacture it at scale?
This is not a demand that exploratory research produce a fielded weapon next year. It is a demand for an honest chain of evidence, with the burden of proof rising as a project approaches procurement. A technically successful experiment can justify further research without being presented as a deployable military capability.
The second test: a migrated network is not necessarily a protected mission
The defensive side has its own accounting problem. NSA says that new commercial National Security Systems must support quantum-resistant algorithms beginning in 2027 and that incompatible legacy systems are to be phased out by 2030. The department’s post-quantum strategy sets broader milestones: support by the end of 2030 and use by the end of 2031, with specified exceptions. These deadlines are necessary. Yet an inventory can show impressive compliance while hiding a weak dependency that a mission cannot do without.
I tested that logic in a deliberately simple constructed model: twelve generic assets, two benign mission-like services, and two configurations in which ten assets had migrated. Both dashboards read 83.3 percent. In one configuration, the unresolved assets lay outside the two services’ critical dependencies, so both security claims remained supported. In the other, an unresolved shared dependency sat on both paths, leaving neither claim supported under the declared profile. Even eleven of twelve assets could give the wrong reassurance if the last exception were the shared component.
This is a counterexample, not an assessment of any Pentagon network. It shows why a migration percentage cannot, by itself, certify a warfighting service. A satellite, radio, aircraft, and forward command post may each depend on the same identity authority, signing key, trust service, or recovery image. Counting platforms separately can conceal the one shared element that decides whether the mission remains supportable.
The risks grow when a system operates disconnected. A valid signature can authenticate the signing key; it does not necessarily establish whether the key remains authorized when the object is finally used. A platform may be unable to obtain a fresh revocation status. A restored image may bring back a legacy cryptographic profile that the migration was designed to retire. The computer boots, the link returns, and the mission’s security assumption has quietly changed.
The NIST migration project rightly emphasizes cryptographic inventories, interoperability, and benchmarking. Those are foundations, not substitutes for a mission-thread check. Program offices should identify each priority service’s cryptographic dependencies and report whether its security requirements remain supported under the actual software, firmware, trust anchors, operational conditions, and planned disconnected interval. “Not demonstrated” needs its own status: it is neither proven compromise nor defensible assurance.
Make the scorecard hard to fool
The Pentagon does not need one new office to grade quantum computing and post-quantum migration together. DARPA’s hardware teams and the officials responsible for cryptographic readiness should keep their separate standards. They do need a common discipline: state the operational claim, identify the assumptions, test the weakest dependencies, and record what the evidence actually permits one to conclude.
For a quantum-computing application, that means a documented classical comparison, independent experimental validation, and a plausible manufacturing path. For a post-quantum mission thread, it means more than a completed asset count: simulate the loss of a shared verifier, delay a revocation update, reconnect with a stale but correctly signed message, and restore an older system image. Record which essential functions can continue, which authorities must narrow, and whether the recovered configuration still meets the approved cryptographic profile.
There is a sensible objection: capable engineers already perform verification, configuration management, and recovery exercises. Additional paperwork could absorb time without improving decisions. So, compare the proposed mission-thread view against existing reviews using the same benign test cases. Measure unsupported approvals, unnecessary rejections, review effort, and time to a justified decision. If the new view adds nothing, do not institutionalize it.
America should pursue powerful quantum computers and move quickly to replace vulnerable cryptography. The challenge is to avoid awarding either effort a passing grade for a number that conceals what matters. A machine must deliver a result the defense industrial base can validate and use. A migrated network must still support the mission when a link fails or a system recovers. The warfighter’s scorecard is the proof that survives both tests.
Burak Oktenli is an independent researcher based in Washington, DC. He holds a bachelor's degree in Computer Science and Engineering from the University of South Florida and an MBA, and is completing a Master of Professional Studies in Applied Intelligence at Georgetown University. His work focuses on defense technology, AI assurance, and dependable systems.
The Unfinished Reform
By Mark W. Castillon • RealClearDefense
Winning the Data Advantage
By Turin Pollard • RealClearDefense
The Pentagon’s Quantum Race Needs a Warfighter’s Scorecard
By Burak Oktenli • RealClearDefense
The F/A-XX and the AIM-260 Reclaim the Perimeter
By Bruce Allen Lubbering • RealClearDefense
Iranian Cyber Operations
By Michael Groen • RealClearDefense
Winning the Data Advantage
By Turin Pollard • RealClearDefenseThe F/A-XX and the AIM-260 Reclaim the Perimeter
By Bruce Allen Lubbering • RealClearDefenseWinning the Data Advantage
By Turin Pollard, RealClearDefenseThe F/A-XX and the AIM-260 Reclaim the Perimeter
By Bruce Allen Lubbering, RCD
F-22 Pilot Directs CCA in Flight as ‘Airborne QB’
By Stephen Losey, Air & Space Forces