State Level Cyber
Last updated 04:50 PM EDT • Read time: 4m
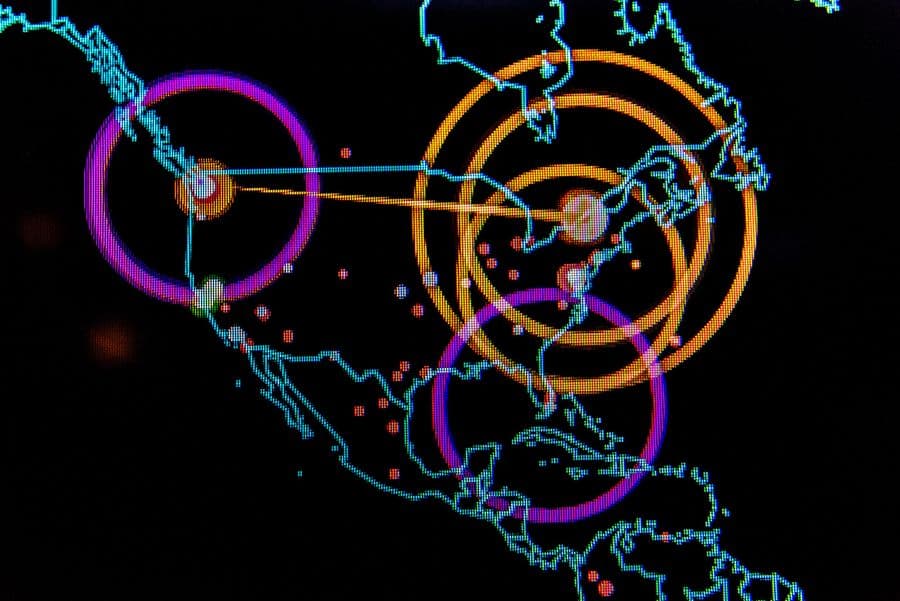
With Cyber Attacks Increasing in Frequency is a Potential New State Level Solution the Answer?
Our world is an ever-changing set of circumstances and associations. Who we count as allies, enemies, and which countries we choose to maintain so-called “strategic associations” with seems to change faster than political approval ratings during campaign season.
With heightened concerns regarding our national security in light of the recent aggressions between America and Iran, as well as the complicated diplomatic dance between the Trump administration and the North Korean regime, in addition to the seemingly never-ending media parroting of the grand Russian scheme to manipulate America, the way we respond to threats in the technological age against our municipal, state and federal government requires fluid responsiveness more than at any other time in nation’s history.
Luckily, that line of thinking has not seemed to be lost on some legislators on Capitol Hill, and despite the historic bickering that is currently occurring involving the historic impeachment and possible removal from office of President Trump, a move that would draw a permanent line dividing ideologues in America, a group of Senators recently introduced the bi-partisan supported Cybersecurity State Coordinator Act (CSCA) of 2020.
The bill, which is sponsored Senators Maggie Hassan (D-NH), the top Democrat on the Senate Homeland Security Committee Gary Peters (D-MI), John Cornyn (R-TX) and Rob Portman (R-OH), on its surface seems to be an applaudable effort by the two parties to establish a state-level, federally funded program that addresses the broad issue of cybersecurity on a more localized level in coordination with the Department of Homeland Security’s Cybersecurity and Infrastructure Security Agency (CISA).
In a recent statement, the CSCA's lead sponsor, Senator Hassan, stated. "Cyberattacks can be devastating for communities across our country, from ransomware attacks that can block access to school or medical records to cyberattacks that can shut down electrical grids or banking services. The bipartisan bill I introduced would take a big step forward in improving communication between the federal government, states, and localities, as well as strengthening cybersecurity preparedness in communities across the country.”
Keeping government agencies, state level financial institutions, and even private citizens safe is a nuanced job that presents its own specific set of challenges regionally. Over the past several years, attacks against state and local governments have increased in frequency. In fact, according to a report from cybersecurity firm Emsisoft, 2019 saw ransomware attacks hit “113 federal, state and municipal agencies, 764 healthcare providers, and 89 school districts and universities.” Emsisoft also described the attacks as an "unprecedented and unrelenting barrage."
Among these attacks were the year end incidents occurring in Pensacola, Florida; Galt, California; New Orleans, Louisiana; and St. Lucie, Florida. The Pensacola attack on December 7th, which is thought to have been carried out by a group known as “MAZE,” affected internet servers, email systems, telephone communications and the online payment systems used by the cities sanitation department and Pensacola Energy.
Another new wave of attacks may be on the horizon as well, in just the past few days, a new warning from CISA regarding the possibility of an increase in attacks utilizing the malware strain known as Emotet seemed to foreshadow further havoc for Americans.
The CSCA can help possibly accelerate the level of preparedness in the case of some states that may have fallen behind on cyber-preparedness or failed to properly prioritize the issue. Some states have already been working for years at a feverish pace to address the matters related to both cybersecurity and the protection of our data online.
Just this month, state level legislation went into effect in California known as the California Consumer Privacy Act (CCPA) that requires companies that store the personal data of at least 50,000 people or other entities that earn at least half their money by selling consumers' personal information to provide expanded protections for that data under threat of potential penalties that would be issued by the California attorney general against businesses that fail to comply.
As advanced as we may think we have become technologically, in reality, we are still living in the embryonic states of the Cyberwarfare age. As countries seek to increase the frequency and severity of their attacks against the United States at all levels of government, legislators across the country must reach across the aisle to work together in ensuring that America remains a step ahead of cyber threats at all times and can protect herself.
Julio Rivera is a business and political strategist, the Editorial Director for Reactionary Times, and a political commentator and columnist. His writing, which is focused on cybersecurity and politics, has been published by websites including Townhall, The Hill, Newsmax and American Thinker.
The First Test of Peace Lies in Ukraine's Borderlands
By Dennis T. Cosgrove • RealClearDefense
The VFW’s Gambling Addiction Victimizes Veterans
By Jack Yoest • RealClearDefense
Superintelligence Exposes a Gap in the Law of Delegated Authority
By Sue Ghosh Stricklett • RealClearDefense
When the Network Goes Dark, Who Controls the Battlefield?
By Jonathan K. Corrado • RealClearDefense
We Cannot Build Tomorrow's Weapons With Yesterday's Alloys
By Joseph F. Krause • RealClearDefense
When the Network Goes Dark, Who Controls the Battlefield?
By Jonathan K. Corrado • RealClearDefense
Air Force Should Buy 250 Blended-Wing Tankers, as 2027 Demo Looms
By A&SF Mag.
Long Deployments to Be Navy Standard For Next Couple Years
By Mongilio, USNI NewsWhen the Network Goes Dark, Who Controls the Battlefield?
By Jonathan Corrado, RCD
Marines Deploy Neros Archer Drone in Live Fire Exercise for First Time
By USNI News